Trust
How we protect your clients’ data.
The things your clients share with you should stay private, encrypted, and yours. Here, plainly, is how Grove keeps them safe.
Grove is built so the things your clients share with you stay private, encrypted, and yours. We use the same identity and infrastructure standards as established software companies, and we deliberately keep every coach’s data partitioned so one coach can never see another’s clients.
- Sign-in is handled by Auth0.
We use Auth0, an industry-standard identity provider, to manage logins. Grove never stores or even sees your clients’ passwords, and every protected request is checked.
- Your practice is isolated from every other coach’s.
Every piece of data is tied to your Practice and filtered at the database layer on every query. One coach can never read another coach’s clients, notes, or messages, and no one outside the coaching relationship, including an employer who may be sponsoring the coaching, can see an individual client’s information. This is enforced in code, not just by a setting.
- Sage applies text redaction before processing.
Before coaching text is sent to Anthropic for Sage, Grove replaces known coach and client names, email addresses, and phone numbers with neutral placeholders and removes account identifiers. Grove restores those placeholders in the result you see. We also redact email addresses and phone numbers in free text, but we do not scan for other names. The remaining text can still include identifying or sensitive details. These controls apply to Sage text processing, not to raw voice audio.
- Voice memos use a separate transcription service.
When voice memos are available and the person recording has given recording consent (the practice for a coach's voice memos, the client for their own), Grove stores recorded coach and client audio in AWS S3 and sends the actual audio to OpenAI for transcription. Voices and spoken names are not de-identified. Audio is kept for 90 days after sending, then deleted; the transcript remains with the message. Voice-memo transcripts are not supplied to Sage. Recording consent is separate from Sage AI consent, and typed messages are an alternative. See the Privacy Policy for details.
- No one is quietly reading client content.
Our application logs record activity and IDs, not the contents of messages, check-ins, or notes. We have no internal tools that surface what your clients write, and the production database is not openly accessible. There is no standing way for anyone, including the Grove team, to browse client content.
- Sessions held in Grove are transcribed only if both sides agree.
A video session in Grove can produce an audio transcript. It is never a video recording. Transcription runs only when you have turned it on for your practice and your client has opted in as well, and both of those start off. Your client is told plainly on the join screen before joining, and can always join without it. The call itself runs on Daily, our video provider, which keeps its own copy of the transcript.
- A session transcript becomes a note only after you review it.
The transcript is stored with the session, and inside Grove only you can read it. Nothing is drafted until you ask for it, nothing is saved until you approve it, and you can discard the draft instead, in which case no note is created. Agreeing to a transcript is not the same as agreeing to Sage: that is a separate consent, and a draft needs both.
- Clients who never sign in are held to the same standard.
You can keep a client in Grove who has no Grove account and never logs in. Same practice isolation, same encryption, same absence of internal browsing tools. For that person you are the data controller and our Terms say so, and because there is no one for us to ask, Sage stays off for them until you turn it on and attest that you have their knowledge. If they later join Grove, the record is preserved and control of it, including the AI setting, transfers to them.
- Your booking page collects very little, and shows nothing about your clients.
A visitor gives a first name, an email address, optionally a last name, the time they picked, and the answers to any form you attached. The page itself shows only what you published: your practice, your session types, your own testimonials and credentials. No client of yours is listed or countable from it. Paid bookings run through your own Stripe account, so the charge is on your business and card details never touch Grove. The links we email afterwards open from a long random token rather than a login, and we store only a hash of it, so a live link cannot be rebuilt from our database.
- Client email carries your practice, and we are straight about how.
The sender name in your client’s inbox is your practice name, the letterhead is your logo and accent color, and Grove is a footer line. The mail is still sent by Grove on your behalf: the sending address stays under our verified grove.coach domain, which is what keeps delivery reliable. We do not send from your own domain today. If your branding cannot be resolved for any reason, the mail still goes out with Grove’s header rather than being held back.
- Encrypted in transit.
All traffic runs over HTTPS (TLS 1.2 or higher), and anything insecure is redirected to a secure connection. Nothing your clients send travels in the clear.
- Encrypted at rest.
The production database and uploaded files are encrypted at rest using managed keys. On its own, the raw storage cannot be read.
- Hosted on AWS, database kept private.
Grove runs on Amazon Web Services. The database lives on a private network and is not reachable from the public internet. Secrets and credentials live in a managed vault, never in our code.
- Backed up every day.
The database is backed up automatically with retention, so data can be recovered.
- Maintained for security.
We monitor our software dependencies for security patches automatically, and an extensive automated test suite runs before any change reaches you.
- You stay in control.
Clients can delete their account and data. Role-based access means coaches, clients, and admins each see only what they should. Consent is part of the onboarding you and your clients complete.
Love how you shared this and connected it to how Grove functions using AI as a tool while also protecting client confidentiality.
Grove is a coaching platform, not a medical records system. It is a good home for the wellness context a client chooses to share with you, their goals, reflections, check-ins, and the notes that help you coach them well, all encrypted and private.
Grove is not intended for storing protected health information (PHI) or formal medical records. If your work involves clinical records such as diagnoses, lab results, or treatment notes, those belong in a system designed for that. A good rule of thumb: collect only the context you need to coach, and keep clinical records elsewhere. For the personal context your clients share in the normal course of coaching, the protections above apply.
Your practice data is yours, in both directions. Grove imports your existing client list from any CSV, and the exit works the same way: ask us at hello@grove.coach and we will provide a complete export of your practice data, in open formats, usually within a few days. We are exploring a self-serve export as well. You should never need permission to leave your own tools.
And because every coach who lived through a platform shutdown knows to ask the harder question: if Grove ever winds down, we commit to at least 90 days of advance notice, a working export path through the very end, and hands-on help moving your practice somewhere good. We wrote about why this matters in What happened to Nudge Coach?
Questions welcome
Security should be legible, not a black box. If you want more detail on any of this, or you have a specific concern about a client’s information, reach out and I will walk you through it.
hello@grove.coach·Privacy & terms
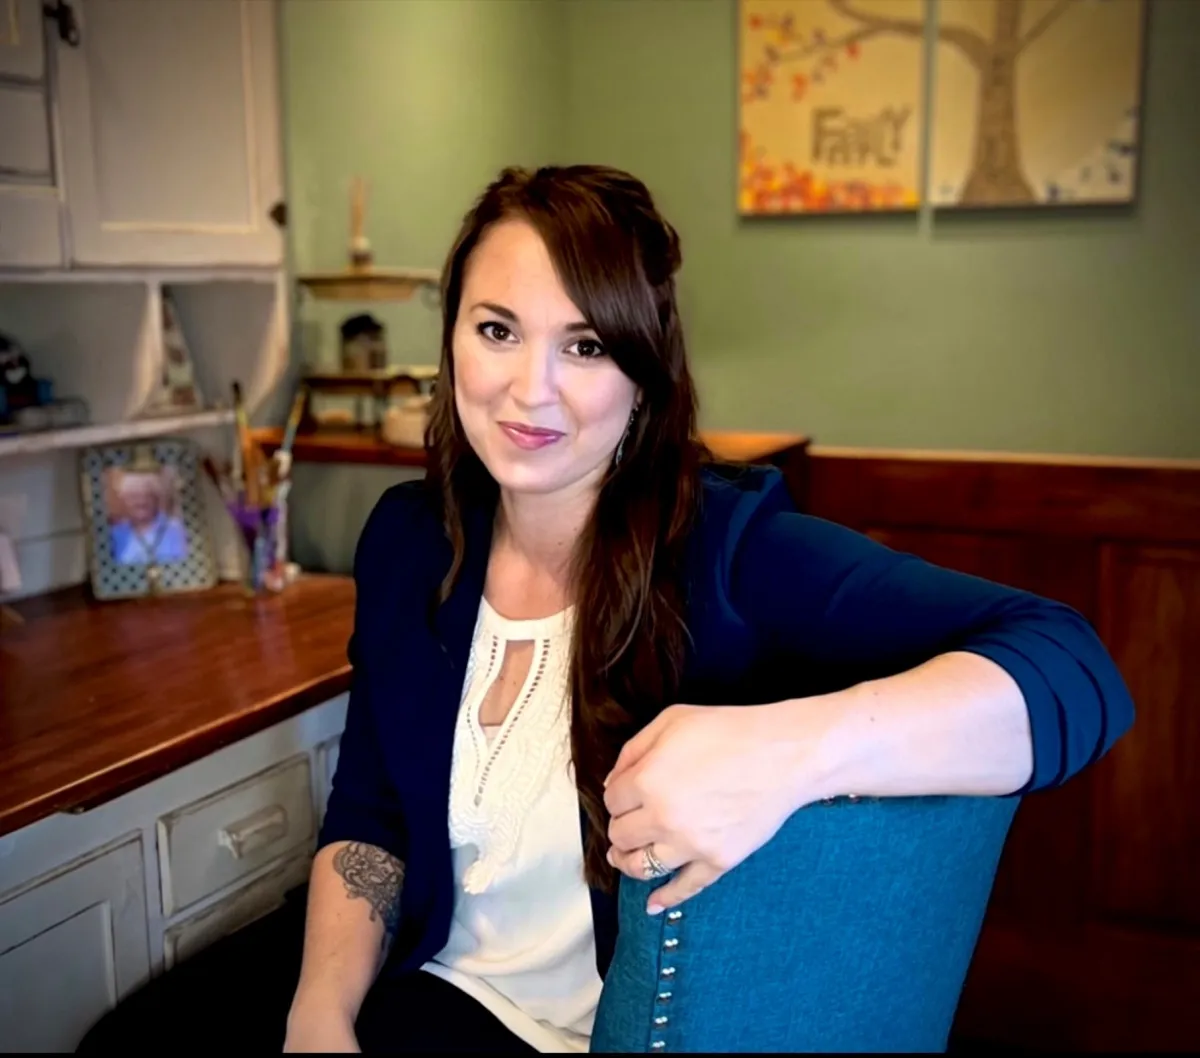
Beth Richardson, Founder, Grove Coach